Supply Chain Vulnerability: The Optimizely Compromise Exposes Global Digital Infrastructure
What Happened?
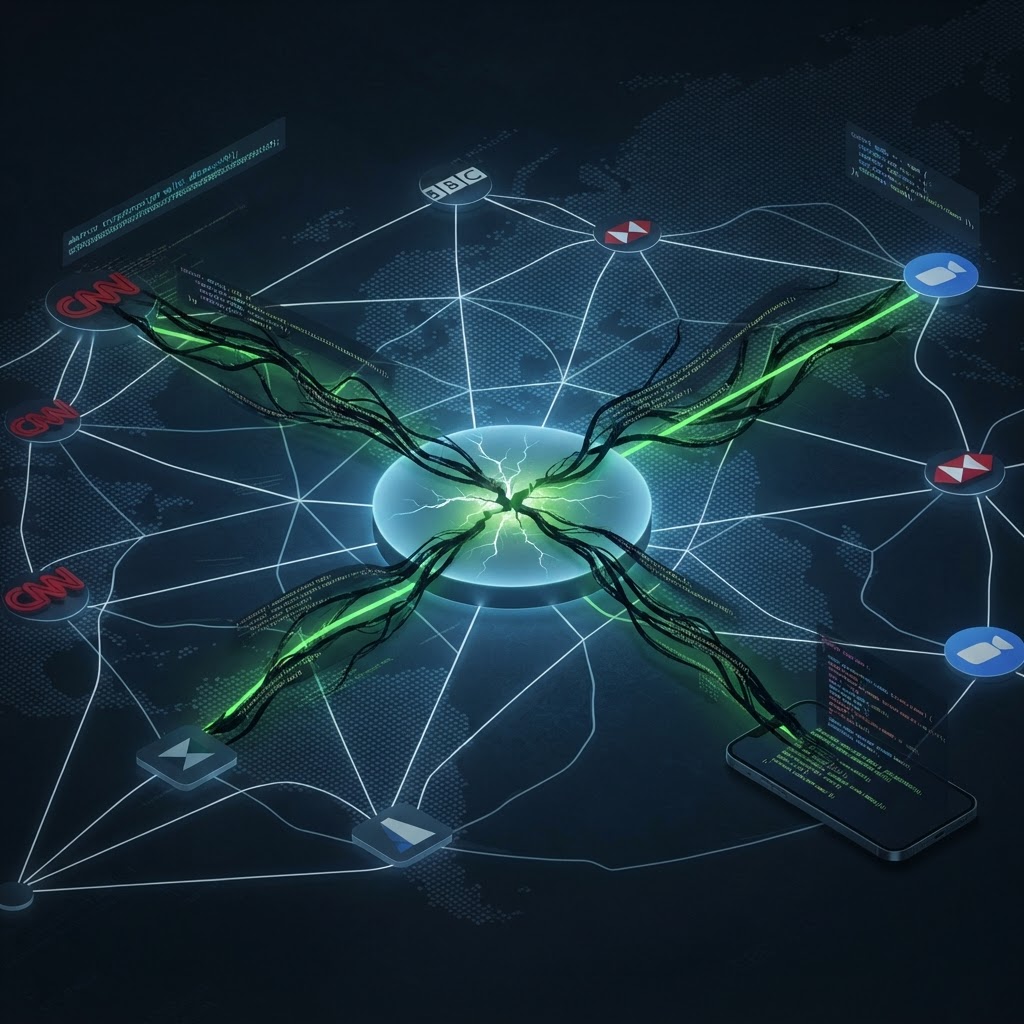
On November 16, 2026, attackers successfully breached the Optimizely Web experimentation platform, leveraging its content delivery network to inject malicious JavaScript across 178 high-profile websites, including CNN, BBC, HSBC, and Zoom.
By compromising the Project JavaScript (projectJS) feature, threat actors bypassed standard security perimeters, directly impacting the browsers of unsuspecting end-users. The campaign enabled persistent data exfiltration, including payment card skimming and the deployment of advanced iOS exploit kits known as Coruna and DarkSword.
Why It Matters
This incident represents a significant escalation in supply chain attacks, moving beyond traditional software updates to the exploitation of dynamic marketing and experimentation tools. Because these scripts are often whitelisted by security policies, they remain invisible to many standard defenses.
The targeting of iOS devices via specific exploit kits signals that this threat actor is highly sophisticated, aiming not just for financial skimming but for long-term device persistence. It highlights a critical blind spot in modern enterprise security: the lack of integrity monitoring for third-party scripts served to customers.
Key Details & Takeaways
- 178 major organizations across sectors including banking, media, and tech were impacted by the malicious script injection.
- Attackers successfully utilized Coruna and DarkSword kits to target mobile users, marking a shift toward cross-platform device exploitation.
- Confirmed cryptocurrency theft via wallet-address manipulation reached at least $7,040 within the initial hours of the campaign.